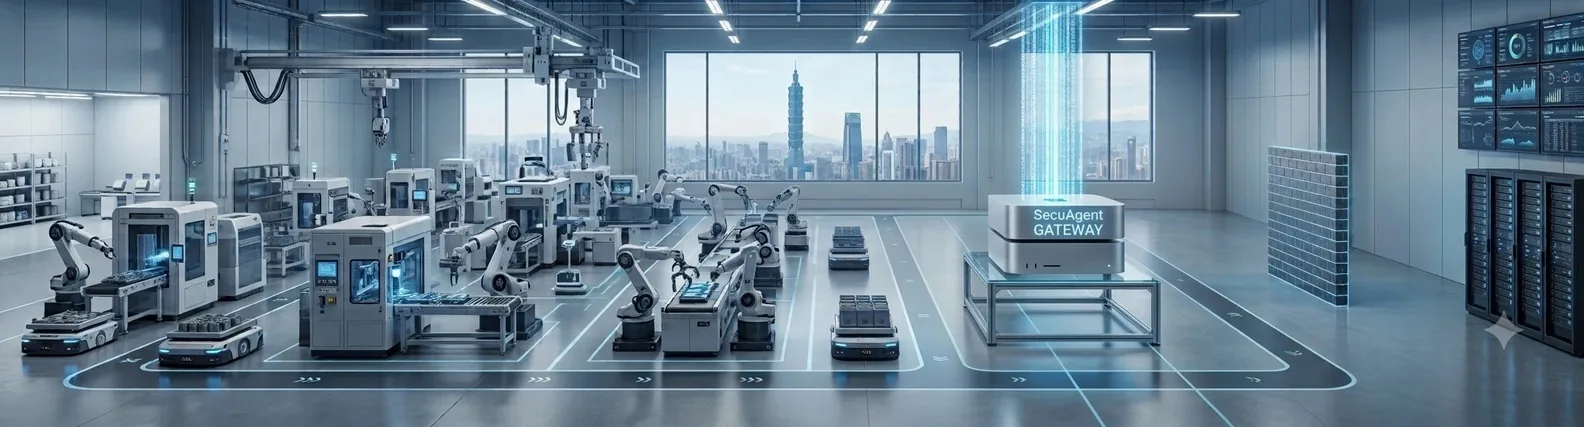
Smart Protection.
Full-spectrum AI governance.
Block security gaps instantly, optimize prompts at the edge, and dynamically assess employee AI proficiency — SecuAgent®'s lightweight governance gateway keeps enterprise AI safe, efficient, and measurable.
Beyond defense —
make AI work better.
SecuAgent evolves from a pure security line of defense into a complete AI governance and efficiency platform.
Smart Security Guardrails
Blocks 14 categories of AI vulnerabilities at the edge, preventing data leaks and prompt injection attacks; four-dimensional RBAC/ABAC authorization with fail-closed defaults keeps you compliant.
Edge Prompt Optimization
Automatically improves employee prompt quality, optimizing complex prompts at the edge for more precise AI responses.
AI Competency Data Governance
Generates an anonymized AI competency matrix report, visualizing company-wide AI usage levels and efficiency gains.
Compute, Security, Budget.
Three mountains — each steeper than the last.
2026 marks the global explosion of AI agents — but Taiwan's 1.6 million SMEs face three critical governance challenges, sharpened by tightening AI Basic Act and Personal Data Protection Act rules. Low cost, high privacy, leak-proof, and governable are now non-negotiable for enterprise AI infrastructure.
Bill Shock
Cloud APIs are billed by usage — employee misuse or poor scheduling makes month-end bills unpredictable. Buying your own hardware just trades that for depreciation and ops hell.
Data Leakage
Finance, healthcare, and retail sit on troves of personal data and trade secrets — yet employees send unredacted data straight to public cloud APIs, leaving privacy fully exposed.
Governance Chaos
Without unified prompt management or model monitoring across departments, AI output quality is inconsistent, and switching models means rewriting code.
Secure, Smart, Cost-Saving.
One platform, three lines of defense.
From the edge to the cloud, SecuAgent delivers a complete AI governance chain — so frontend teams can ship safely within days.
SecuAgent Endpoint Protection
A three-path transparent network interception architecture: system-level TUN/WFP capturing desktop app traffic (e.g. the Electron build of Claude) over HTTPS, a browser extension intercepting web chats like claude.ai, and a CLI daemon monitoring developer terminal logs — ensuring 100% of data passes through the redaction engine.
system → utun4 / WFP kernel-level TLS MITM
browser → Chrome MV3 content script
cli → Rust daemon · 800ms polling
// 100% coverage of all egress channels
Smart Routing, Intent-Driven
Dispatches each query to an 8B/26B/70B tier model based on complexity and sensitivity, with millisecond-level latency/failover switching invisible to the frontend.
Millisecond Dual Safety Filtering
SecuGuard (developed in-house by SecuAgent, F1=0.9653, false-positive rate of just 0.19%) cross-validated with IBM Granite Guardian 3.0, covering 14 harm categories including personal data leaks, IP infringement, and code-interpreter abuse — while simultaneously blocking jailbreak attacks and evaluating hallucinations.
Golden Prompt Asset Library
Version control, permission management, automated optimization, and Prompt Injection protection, closing the loop with output quality scoring.
Kubernetes + KEDA Autoscaling
Node pools are partitioned by model family, with weighted fair queueing across Enterprise/Paid/Free tenant tiers so no single tenant starves the shared GPU pool — backed by automatic cross-region DNS failover.
Zero-Cost Repeated Prompts
Redis + embedding similarity matching hits cache directly without touching the GPU; paired with an idempotency-key billing pipeline for zero-error usage and charges.
Permissions Are the Retrieval Boundary
The knowledge base is split into independent partitions by department and sensitivity level. Access rights determine what can be retrieved in the first place — not filtered out after the fact.
Fail-Closed × Tamper-Evident Audit
Four-dimensional RBAC/ABAC cross-authorization defaults to "access denied" whenever any attribute is missing. A hash-chained audit log plus crypto-shredding satisfies tamper-evident audit trails and the "right to be forgotten" at the same time.
From Chaos to Control.
Enterprise-grade AI governance, delivered in one step.
SecuAgent isn't just a technical upgrade — it's a complete leap in AI governance maturity.
Cloud-Native × Edge Protection.
Every layer has clear, measurable specs.
A complete technical chain from endpoint to cloud, with every step engineering-verified.
International Certifications.
Building a long-term foundation of trust.
SecuAgent is mapping a certification path toward the international security and AI governance standards below, progressively strengthening its enterprise trust foundation。
ISO/IEC 27001
ISMS Information Security Management
SSDLC / SBOM
Built & executed by our internal engineering team
OWASP ASVS / Pen Test / Vuln Scan
Built & executed by our internal engineering team
ISO/IEC 42001
AI Management System
ISO/IEC 27701
PIMS Privacy Information Management
It's not whose model is bigger —
it's whose governance is designed more thoroughly.
Everyone claims to be "secure." The difference is decided at the design stage — bolted on after the fact, or built in from day one.
Still have questions?
We'll answer them here.
The questions enterprises ask most before adopting an AI security gateway — answered directly and honestly.
SecuAgent is an enterprise AI security gateway built for organizations that need to safely handle personal data and trade secrets between cloud LLMs and on-premises systems. Its core capabilities are edge-based data redaction, intelligent request routing, and hybrid cloud/on-premises compute scheduling — letting enterprises adopt AI safely on a predictable budget.
The redaction engine combines regex pattern matching with lightweight NLP to detect and mask personal-data signatures in real time. The guardrail layer adds cross-validation between SecuGuard (F1=0.9653, 0.19% false-positive rate) and IBM Granite Guardian 3.0, reducing the risk of any single model's blind spots. We recommend using the 14-day free assessment to tune and validate against your actual conversation patterns.
No. The knowledge base uses multi-RAG partitioning, split into independent partitions by department and sensitivity level, so access rights directly define the retrieval boundary rather than filtering results after the fact. This is paired with four-dimensional RBAC/ABAC authorization (department, role, clearance level, need-to-know) — if any authorization attribute is missing, the system defaults to "access denied" (fail-closed), so a misconfiguration never leaves you exposed.
We offer a 14-day free assessment, with our engineering team guiding you from PoC to production. Endpoint protection intercepts transparently at the system, browser, and CLI layers, so employees don't need to change their existing habits. A third-party penetration test is completed before go-live.
We use a hard quota circuit-breaker plus a flat monthly rate, avoiding the "bill shock" of usage-based cloud API billing. Actual pricing depends on your usage volume and deployment model (on-premises or hybrid cloud) — book an assessment for a concrete quote.
Not yet. ISO/IEC 27001, ISO/IEC 42001, and ISO/IEC 27701 are all part of our planned roadmap, while SSDLC/SBOM and OWASP ASVS/penetration testing/vulnerability scanning are already integrated into our engineering process — we clearly label planned items as "planned," not obtained, and will update this page as each is achieved.
We resolve this with crypto-shredding: every audit event is chained with hashes, so any tampering is immediately detectable, satisfying long-term retention and non-repudiation requirements. A deletion request removes only that data subject's unique decryption key — the historical trail stays fully intact, but the personal data itself can never be recovered. If litigation or an investigation is underway, deletion requests are also automatically frozen by our legal hold mechanism.
The three-path interception architecture (system-level TUN/WFP, browser extension, CLI watcher) is designed for company-issued, managed devices, browsers, and dev environments. Fully unmanaged personal devices fall outside standard coverage — if BYOD is part of your environment, we recommend raising it during the assessment.
No vendor lock-in. Smart routing dispatches simple queries to lightweight open-source models and complex reasoning to top-tier commercial models, with millisecond-level automatic failover, and the model deployment layer exposes a unified API wrapper.
Admission Control immediately returns 429 + Retry-After for over-quota requests instead of queuing indefinitely. Human review is only triggered by high-risk actions — external sends, data changes, or highly sensitive content — so ordinary queries are never held up; overdue reviews escalate automatically at T+0/4h/8h/24h. Our engineering team helps investigate false positives and tune rules during onboarding, and for formal SLAs and support response times, we recommend agreeing on specifics with our team during the assessment.
SecuAgent is built specifically for the "low-cost, high-privacy, leak-proof, governable" needs of Taiwan's 1.6 million SMEs, not just large enterprises — the architecture scales resource allocation to tenant size. We recommend a free assessment to confirm the actual complexity and cost fit your situation.
The GPU utilization gain comes from vLLM PagedAttention memory management (from roughly 40% before deployment to 80%+ after). The egress cost reduction comes from JuiceFS local data caching (≥10GB/s NVMe reads, <0.1ms latency), which cuts cross-cloud data transfer. These are internal measurements — actual results will vary with your existing infrastructure and usage patterns.
The guardrail layer intercepts 14 common categories of security threats in real time, capturing and backing up security event logs for subsequent forensic analysis and compliance audits; every deployment passes third-party penetration testing before go-live. Because the system is deployed on-premises, the actual incident-reporting process and liability boundary (e.g., infrastructure security vs. software service) will be clearly defined in the contract and during onboarding.
Yes. SecuAgent automatically optimizes prompts at the edge before they reach the cloud AI — adding clear structure, explicit instructions, and response format constraints — improving output quality across the workforce while cutting wasted compute.
Yes. SecuAgent anonymously analyzes the frequency, complexity, and quality of employee-AI interactions and produces an "AI Competency Matrix" report, giving HR and IT leaders a clear view of company-wide AI proficiency to guide training and measure transformation progress; any small sample group that could be re-identified is automatically merged up to the department level (k-anonymity) rather than simply hidden, and the analysis never reconstructs what any individual actually asked — so management gets real insight without compromising employee privacy.
Make AI Safety Real.
Starting Today.
A 14-day free assessment to find the deployment plan that fits you. Our engineering team will guide you through the full journey from PoC to production, with a third-party penetration test completed before project close.
Further reading: Who's Reining In Runaway Enterprise AI? The Four Core Functions of an AI Gateway